Enforce downscoping in token exchange for agent-to-agent calls
A Keycloak lab for A2A agents: the token B gets for C follows B's own scopes, not A's, unless you enforce downscoping. Stock run, control run and the fix.
Type the URL of an MCP server. I follow the discovery steps of the MCP spec from your browser and check what a client will find there.
Runs in your browser. Nothing you paste is sent anywhere. Don't paste production private keys.
Run discovery sends plain GET requests from your browser to the MCP URL you typed and to the metadata URLs it finds, with no cookies and no credentials. Nothing goes to iamops.dev and nothing is stored. Anything you paste into the boxes stays on your device.
curl -i https://mcp.example.com/mcpcurl -s https://mcp.example.com/.well-known/oauth-protected-resourcenpx @modelcontextprotocol/inspectorUse a test account and throwaway keys. Do not paste production secrets, session cookies or real users' tokens.
The MCP server URL, or the Protected Resource Metadata and authorization server metadata JSON if CORS blocks the fetch.
Checks follow the authorization part of MCP 2026-07-28.
Paste the WWW-Authenticate value and the JSON from the curl commands. The checks update as you type.
Samples are made with throwaway keys and example.test names. They mean nothing outside this page.
The MCP server URL, or the Protected Resource Metadata and authorization server metadata JSON if CORS blocks the fetch.
Most often the server answers 401 without a resource_metadata hint and has no metadata at /.well-known/oauth-protected-resource, or the resource value differs from the URL clients use.
The server did not allow cross-origin reads. A desktop MCP client does not care about CORS, so this is not a bug in the server. Run the curl commands and paste the JSON.
The newest posts and labs on the same topic, picked automatically.
A Keycloak lab for A2A agents: the token B gets for C follows B's own scopes, not A's, unless you enforce downscoping. Stock run, control run and the fix.
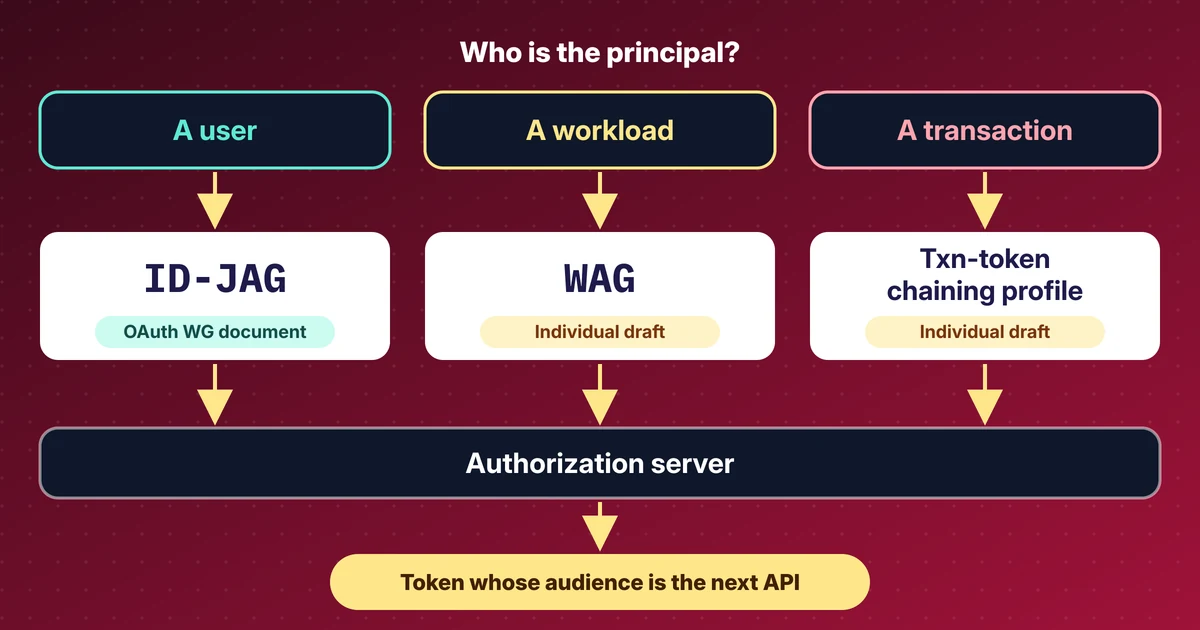
My reading of the IETF 127 OAuth and WIMSE sessions: ID-JAG, the Workload Authorization Grant, transaction tokens and actors, with draft revisions.
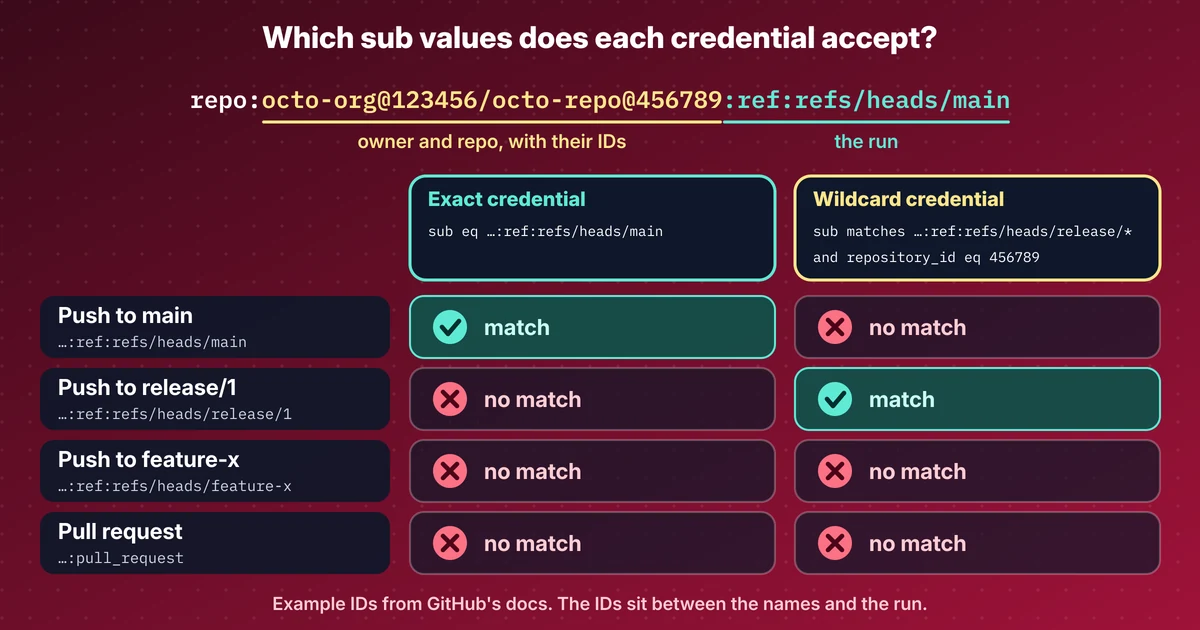
GitHub's default OIDC sub now carries owner and repo IDs, Entra wildcard credentials are still in preview, and WorkOS shipped agent auth. Sources and dates.
How ID-JAG and Cross App Access let a company's identity provider approve AI agent access to other apps, with lab screenshots and the draft's current status.