Enforce downscoping in token exchange for agent-to-agent calls
A Keycloak lab for A2A agents: the token B gets for C follows B's own scopes, not A's, unless you enforce downscoping. Stock run, control run and the fix.
Paste a Security Event Token. I explain each event, the subject it is about and the timestamps, and check it against SSF 1.0.
Runs in your browser. Nothing you paste is sent anywhere. Don't paste production private keys.
The page makes no network request while you work. The only exceptions are the buttons that say Fetch, which call the address you type. Keep real private keys out of any web page, including this one.
Use a test account and throwaway keys. Do not paste production secrets, session cookies or real users' tokens.
A Security Event Token (JWT) as the transmitter sent it, in a push body or a poll response. Optionally paste the transmitter JWK or JWKS to verify the signature.
Event types and formats from OpenID Shared Signals Framework 1.0, OpenID CAEP 1.0, OpenID RISC 1.0, RFC 8417, RFC 9493.
Samples are made with throwaway keys and example.test names. They mean nothing outside this page.
A Security Event Token (JWT) as the transmitter sent it, in a push body or a poll response. Optionally paste the transmitter JWK or JWKS to verify the signature.
A JWT defined in RFC 8417 that says something happened to a subject, such as a revoked session. The OpenID Shared Signals Framework, CAEP and RISC define the event types and how they are delivered.
CAEP events are about live access: sessions, tokens, devices and assurance. RISC events are about account safety: compromised credentials, disabled accounts and recycled identifiers.
The newest posts and labs on the same topic, picked automatically.
A Keycloak lab for A2A agents: the token B gets for C follows B's own scopes, not A's, unless you enforce downscoping. Stock run, control run and the fix.
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
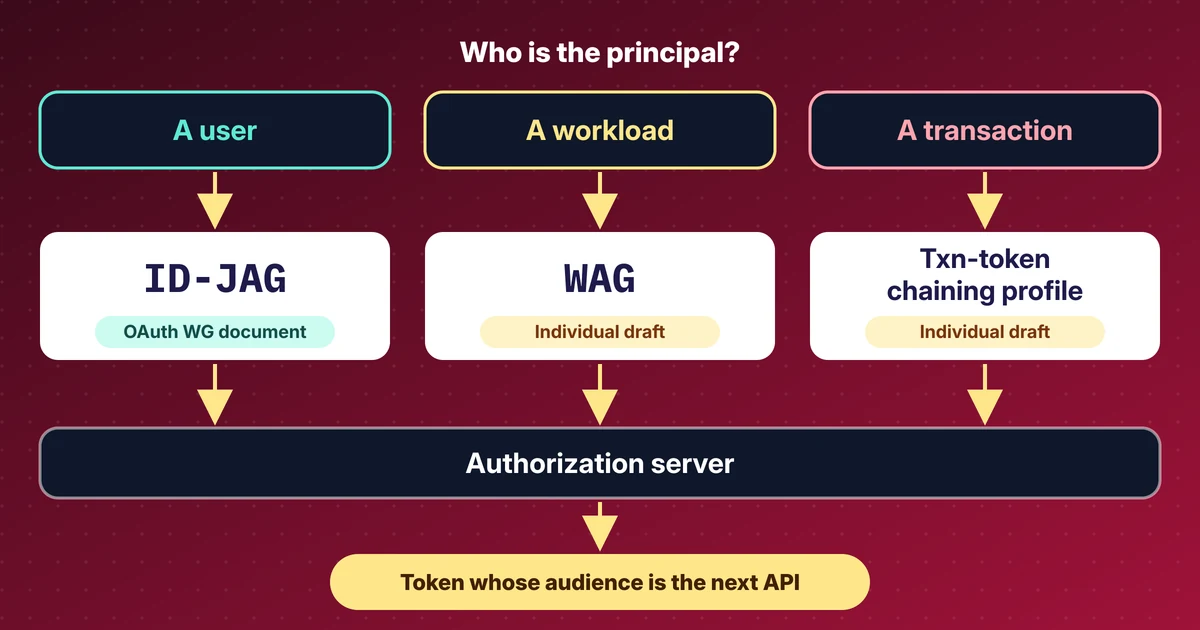
My reading of the IETF 127 OAuth and WIMSE sessions: ID-JAG, the Workload Authorization Grant, transaction tokens and actors, with draft revisions.