GitHub Actions to Azure with workload identity federation: which runs get a token, and why
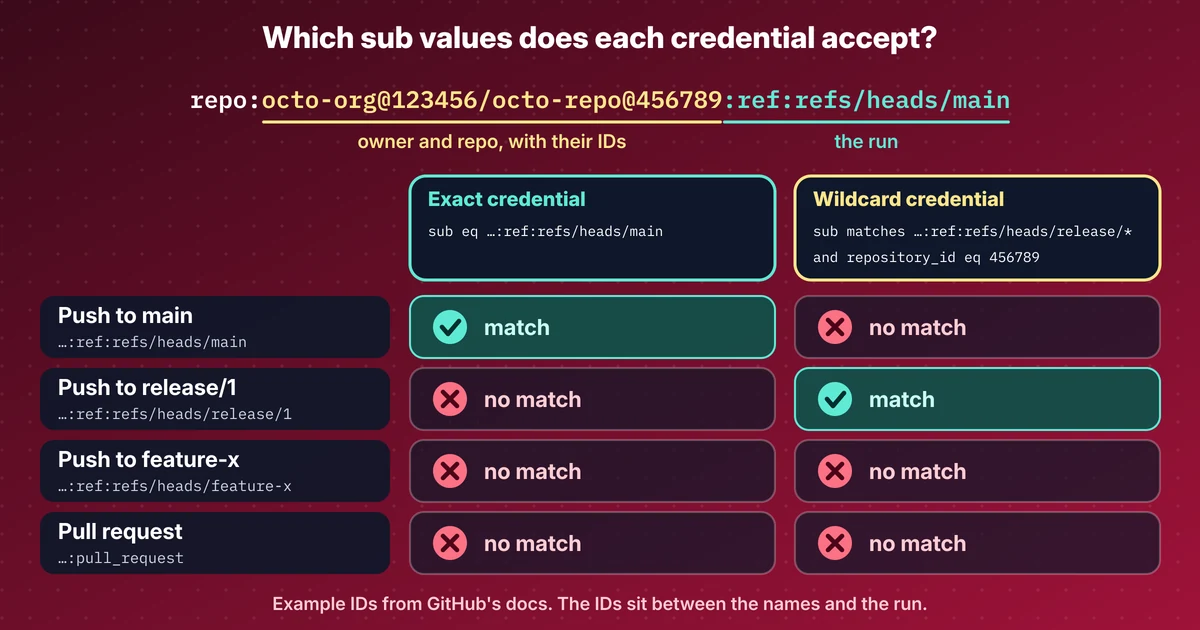
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
No posts in this audience.
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
GitHub's default OIDC sub now carries owner and repo IDs, Entra wildcard credentials are still in preview, and WorkOS shipped agent auth. Sources and dates.
Lab in a test tenant: device-code sign-in, an agent API exchanging the token on-behalf-of with a certificate and no secret, and an unconsented scope failing.
Lab: a Container App agent with a user-assigned managed identity and no secrets gets one narrow app role, receives an app-only token, and the API validates it.