GitHub Actions to Azure with workload identity federation: which runs get a token, and why
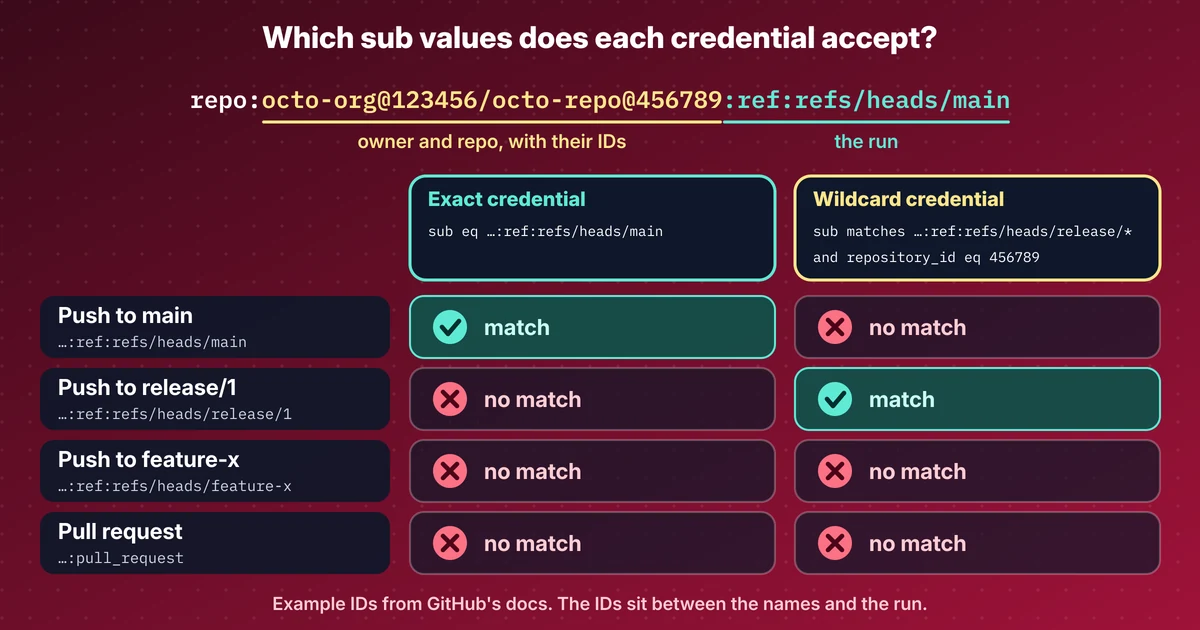
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
Drop a HAR export to list the requests, follow the identity flow, and copy a call as curl. Redaction stays on unless you turn it off.
Runs in your browser. Nothing you paste is sent anywhere. Don't paste production private keys.
The page makes no network request while you work. The only exceptions are the buttons that say Fetch, which call the address you type. Keep real private keys out of any web page, including this one.
mitmdump --set hardump=./capture.harA HAR file holds the cookies, tokens and form data of every request. Capture with a test account, and remove or rotate anything sensitive before you share it.
Use a test account and throwaway keys. Do not paste production secrets, session cookies or real users' tokens.
A HAR file exported from your browser Network tab, or drop the file onto the page. HARs often contain cookies and tokens, so prefer a copy you do not mind keeping on this device. Nothing is uploaded.
Drop a .har file here
Or choose a file, or paste the JSON below. Nothing is uploaded.
Samples are made with throwaway keys and example.test names. They mean nothing outside this page.
A HAR file exported from your browser Network tab, or drop the file onto the page. HARs often contain cookies and tokens, so prefer a copy you do not mind keeping on this device. Nothing is uploaded.
No. Parsing, filtering and redaction run in your browser. Nothing is sent to this site. Still, a HAR often holds session cookies, so prefer a sanitized copy if you share one.
Cookies, Authorization, Set-Cookie, client_secret, authorization codes, tokens, passwords and other obvious secrets, including JWT-shaped values, in the view, in copies and in the sanitized download.
You can copy it as curl, fetch or HTTPie and run it on your machine. This page does not send the request for you, so your tokens stay on the device.
The newest posts and labs on the same topic, picked automatically.
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
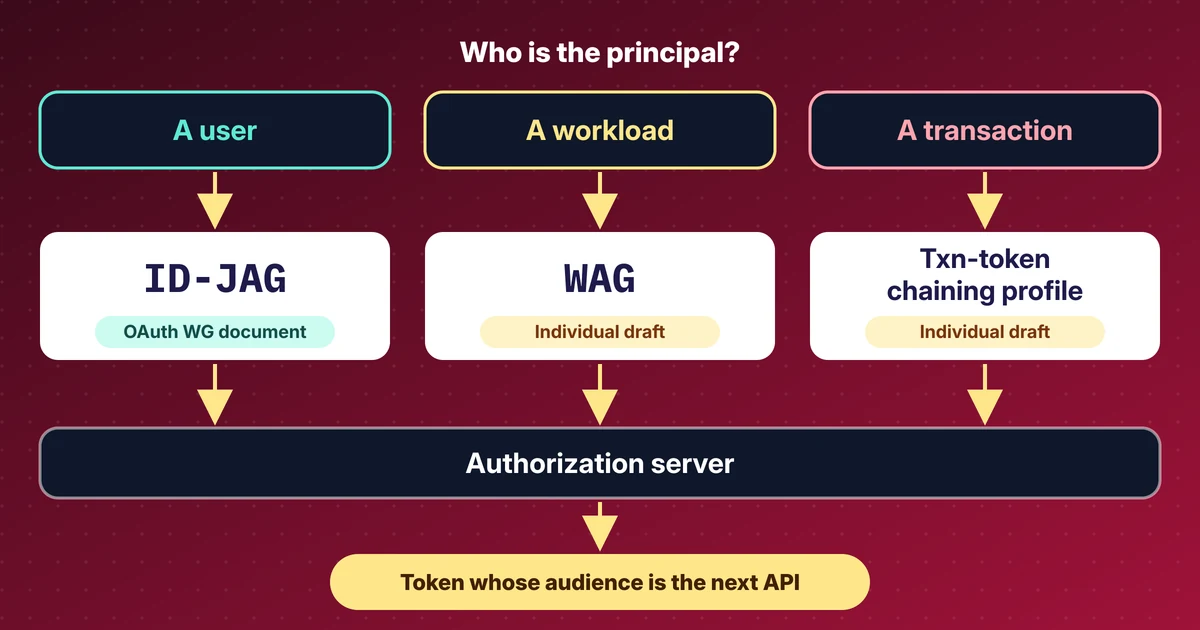
My reading of the IETF 127 OAuth and WIMSE sessions: ID-JAG, the Workload Authorization Grant, transaction tokens and actors, with draft revisions.
GitHub's default OIDC sub now carries owner and repo IDs, Entra wildcard credentials are still in preview, and WorkOS shipped agent auth. Sources and dates.
How ID-JAG and Cross App Access let a company's identity provider approve AI agent access to other apps, with lab screenshots and the draft's current status.