GitHub Actions to Azure with workload identity federation: which runs get a token, and why
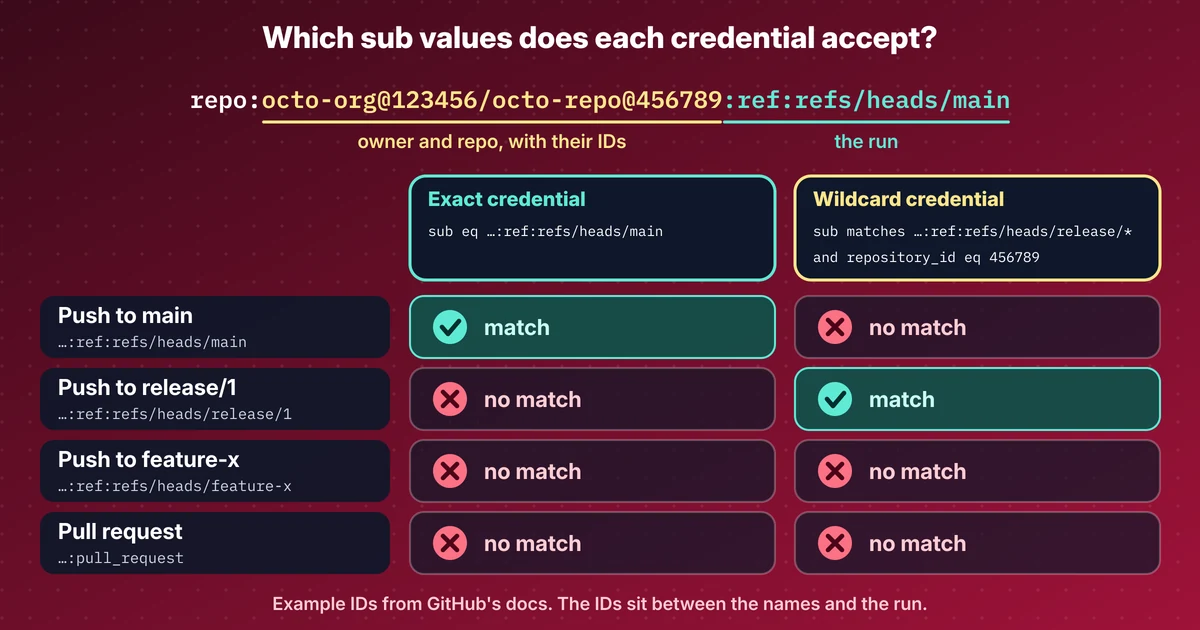
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
Paste a PEM or DER certificate, a chain or a CSR to read the subject, SANs, expiry and chain order. It runs in your browser, so nothing goes to a server.
Runs in your browser. Nothing you paste is sent anywhere. Don't paste production private keys.
The page makes no network request while you work. The only exceptions are the buttons that say Fetch, which call the address you type. Keep real private keys out of any web page, including this one.
openssl s_client -connect example.com:443 -servername example.com -showcerts </dev/nullUse a test account and throwaway keys. Do not paste production secrets, session cookies or real users' tokens.
A PEM certificate, a chain of PEMs, a CSR, or the same data as base64 or hex DER. Include the BEGIN and END lines when you have them. Do not paste a private key.
Samples are made with throwaway keys and example.test names. They mean nothing outside this page.
A PEM certificate, a chain of PEMs, a CSR, or the same data as base64 or hex DER. Include the BEGIN and END lines when you have them. Do not paste a private key.
Paste the text, including the BEGIN and END lines, into the box. DER as base64 or hex also works. The page shows the subject, issuer, SANs, validity, key, extensions and fingerprints.
Certificates are public, and the decoding runs in your browser with no upload. Do not paste private keys into any web page.
The newest posts and labs on the same topic, picked automatically.
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
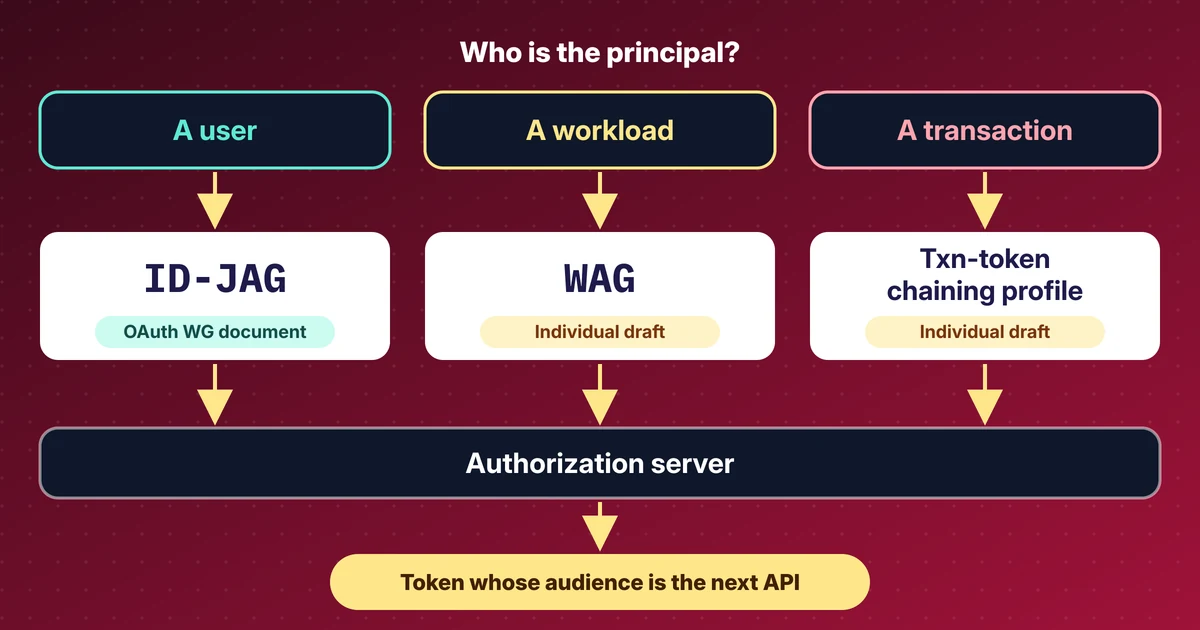
My reading of the IETF 127 OAuth and WIMSE sessions: ID-JAG, the Workload Authorization Grant, transaction tokens and actors, with draft revisions.
GitHub's default OIDC sub now carries owner and repo IDs, Entra wildcard credentials are still in preview, and WorkOS shipped agent auth. Sources and dates.
Lab in a test tenant: device-code sign-in, an agent API exchanging the token on-behalf-of with a certificate and no secret, and an unconsented scope failing.