GitHub Actions to Azure with workload identity federation: which runs get a token, and why
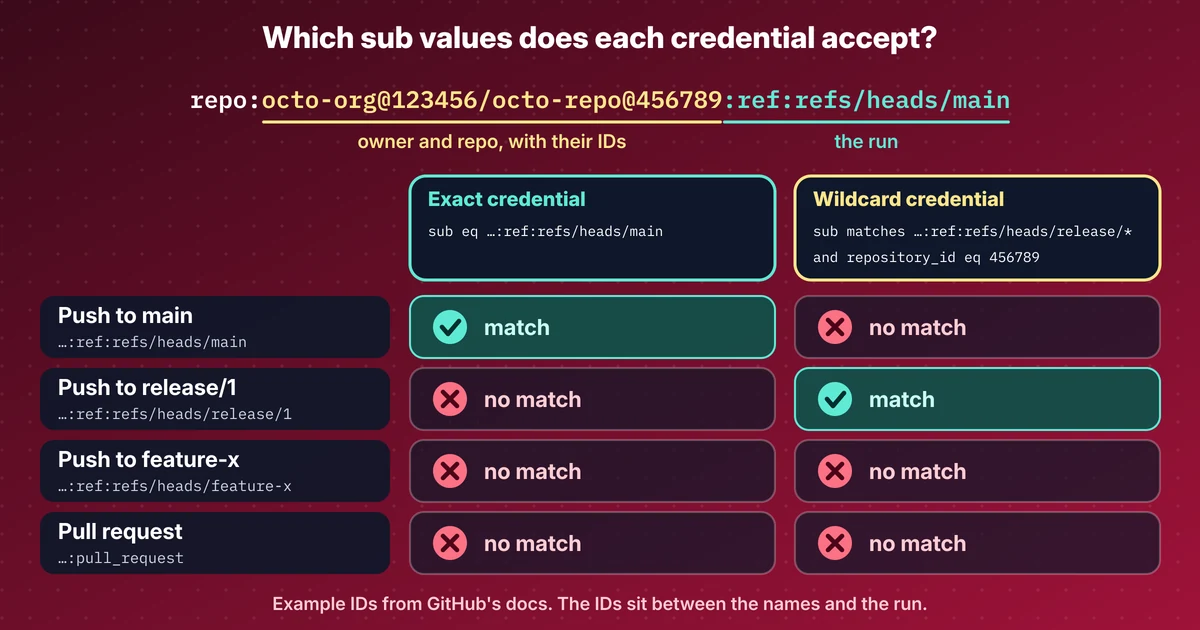
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
Make a code verifier and its S256 challenge, or check a pair you already have.
Runs in your browser. Nothing you paste is sent anywhere. Don't paste production private keys.
The page makes no network request while you work. The only exceptions are the buttons that say Fetch, which call the address you type. Keep real private keys out of any web page, including this one.
Use a test account and throwaway keys. Do not paste production secrets, session cookies or real users' tokens.
Nothing is required to generate a pair. To check a pair you already have, paste the code verifier and the S256 challenge.
Samples are made with throwaway keys and example.test names. They mean nothing outside this page.
Nothing is required to generate a pair. To check a pair you already have, paste the code verifier and the S256 challenge.
Create a random verifier of 43 to 128 characters, take its SHA-256 hash and encode it as base64url. That value is the S256 challenge. This page does it with the Web Crypto random source.
Use S256. Plain sends the verifier in the clear and is only for clients that cannot hash, which is almost never the case today.
The newest posts and labs on the same topic, picked automatically.
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
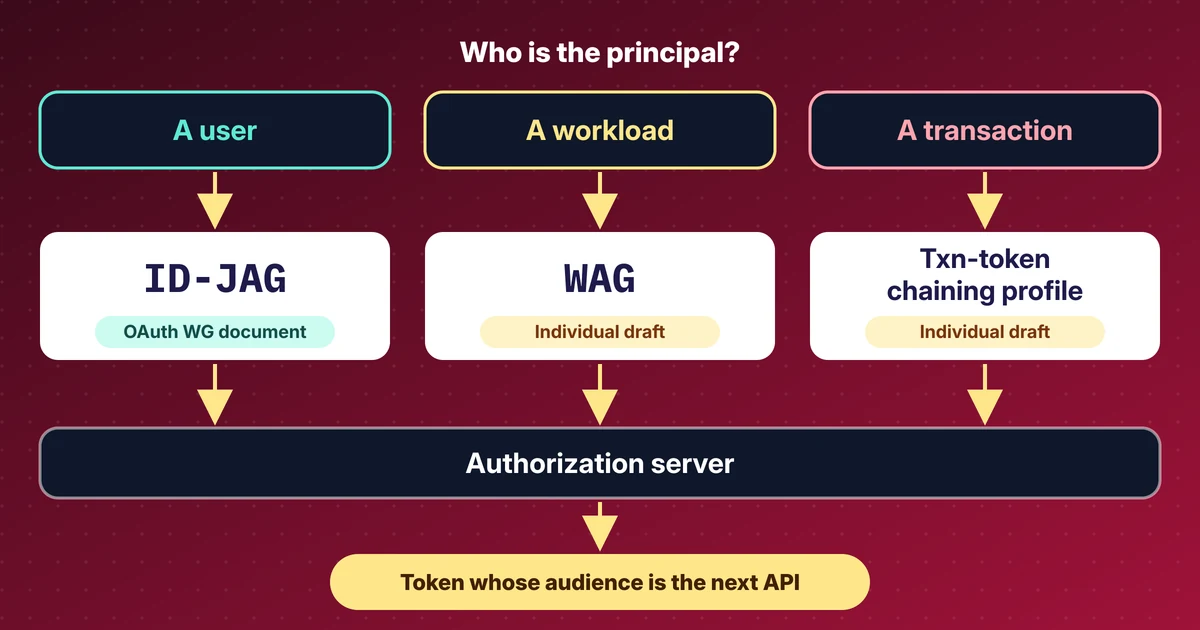
My reading of the IETF 127 OAuth and WIMSE sessions: ID-JAG, the Workload Authorization Grant, transaction tokens and actors, with draft revisions.
GitHub's default OIDC sub now carries owner and repo IDs, Entra wildcard credentials are still in preview, and WorkOS shipped agent auth. Sources and dates.
How ID-JAG and Cross App Access let a company's identity provider approve AI agent access to other apps, with lab screenshots and the draft's current status.