Enforce downscoping in token exchange for agent-to-agent calls
A Keycloak lab for A2A agents: the token B gets for C follows B's own scopes, not A's, unless you enforce downscoping. Stock run, control run and the fix.
Paste an SD-JWT or a presentation with a Key Binding JWT. I split it, decode every disclosure, recompute the digests and show which claims the holder revealed.
Runs in your browser. Nothing you paste is sent anywhere. Don't paste production private keys.
The page makes no network request while you work. The only exceptions are the buttons that say Fetch, which call the address you type. Keep real private keys out of any web page, including this one.
Use a test account and throwaway keys. Do not paste production secrets, session cookies or real users' tokens.
The compact SD-JWT string, including the ~ separators and, if present, the Key Binding JWT at the end. Optionally paste the issuer JWK or JWKS to verify the signature. Line breaks are ignored.
Follows RFC 9901.
Samples are made with throwaway keys and example.test names. They mean nothing outside this page.
The compact SD-JWT string, including the ~ separators and, if present, the Key Binding JWT at the end. Optionally paste the issuer JWK or JWKS to verify the signature. Line breaks are ignored.
A signed JWT where some claims are replaced by salted hashes. The holder sends the matching disclosures only for the claims it wants to reveal. RFC 9901 defines it, and SD-JWT VC builds credentials on top of it.
Its digest is not in any _sd array or ... entry of the signed payload. The disclosure was changed after issuance, was copied from another credential, or the hash algorithm in _sd_alg does not match.
The newest posts and labs on the same topic, picked automatically.
A Keycloak lab for A2A agents: the token B gets for C follows B's own scopes, not A's, unless you enforce downscoping. Stock run, control run and the fix.
Lab: a GitHub workflow signs in to Azure with no secret. I print the sub of six kinds of run and show which credential lets each one in, pull requests too.
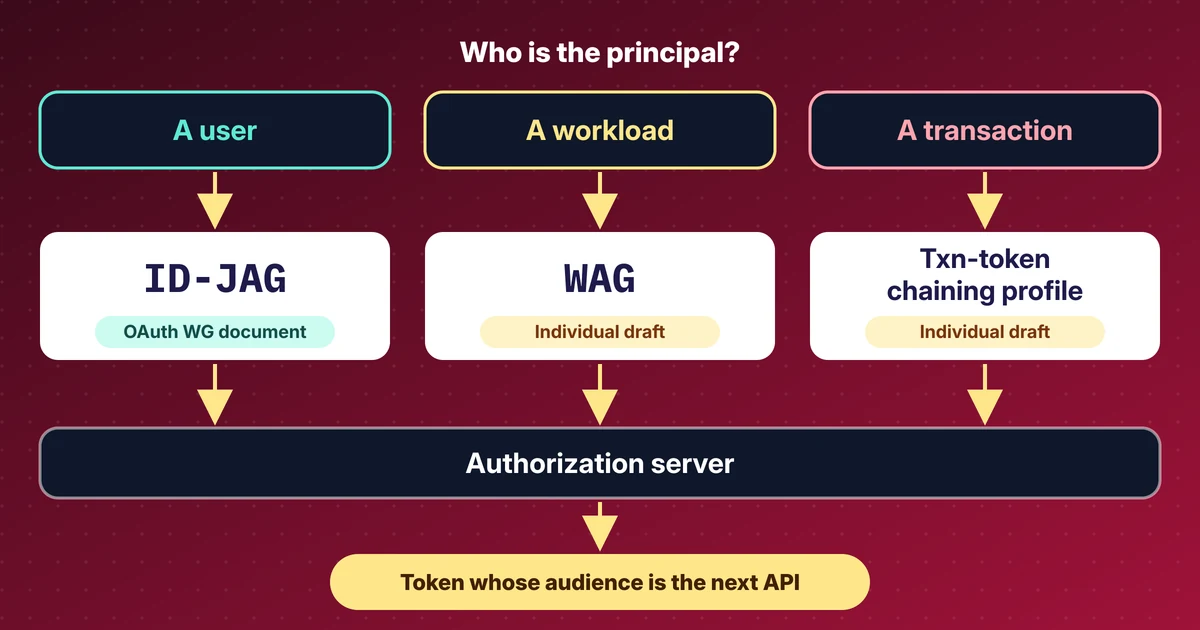
My reading of the IETF 127 OAuth and WIMSE sessions: ID-JAG, the Workload Authorization Grant, transaction tokens and actors, with draft revisions.